AccountingFreelance

Free · 12 questions · about 3 minutes

Is your practice's data security compliant?

Paid tax preparers are required by federal law to keep a written information security plan (WISP) under the FTC Safeguards Rule. This self-assessment checks your practice against the rule's main requirements and shows you exactly what to fix.

Your answers stay in your browser until you choose to email yourself the report.

What you'll get

A draft WISP, written for your firm

  • ✓ A Word document, structured after IRS Publication 5708
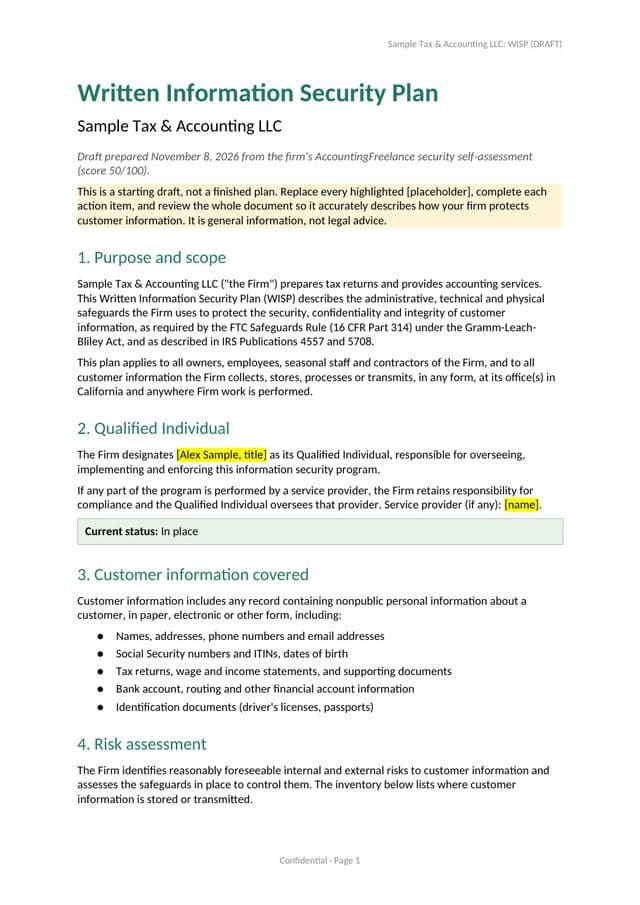
  • ✓ Pre-filled with your firm's details and answers
  • ✓ Color-coded status for every safeguard
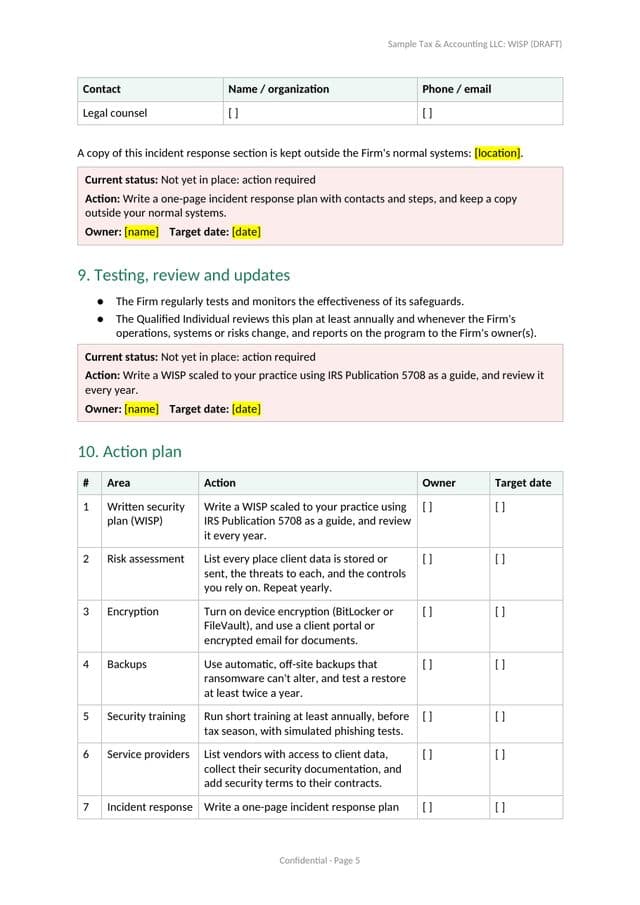
  • ✓ Every gap turned into an action item, plus a sign-off page
Download a sample (fictional firm, .docx)
Sample WISP page showing the action planSample WISP first page
Written security plan (WISP)

1 of 12 · Written security plan (WISP)

Do you have a written information security plan (WISP) that you've reviewed in the last 12 months?

Qualified Individual

2 of 12 · Qualified Individual

Have you named one person responsible for overseeing your security program?

Risk assessment

3 of 12 · Risk assessment

Have you assessed where client data lives (devices, email, cloud, paper) and what could put it at risk?

Multi-factor authentication

4 of 12 · Multi-factor authentication

Is multi-factor authentication (MFA) required on every system that holds client data — email, tax software, cloud storage and remote access?

Encryption

5 of 12 · Encryption

Is client data encrypted on laptops and servers, and sent through a secure portal or encrypted email rather than plain attachments?

Access control

6 of 12 · Access control

Does each person only have access to the client data they need, and are accounts removed promptly when someone leaves?

Backups

7 of 12 · Backups

Are client files and systems backed up automatically to a separate location, with a restore tested in the last 6 months?

Security training

8 of 12 · Security training

Does everyone at the firm, including seasonal staff, get security and phishing training at least once a year?

Service providers

9 of 12 · Service providers

Have you checked the security of vendors that can access client data (IT provider, software, cloud services) and put security terms in their contracts?

Incident response

10 of 12 · Incident response

Do you have written steps for what to do in a data breach, including who to notify (your IRS Stakeholder Liaison, the FTC, clients and your state)?

Updates and monitoring

11 of 12 · Updates and monitoring

Are computers and software kept up to date automatically, protected by antivirus or endpoint protection, and is access to client data logged?

Secure disposal

12 of 12 · Secure disposal

Do you securely delete or shred client data you no longer need, generally within two years of last use unless you must keep it?

0 of 12 answered

Based on the FTC Safeguards Rule (16 CFR Part 314) and IRS Publications 4557 and 5708. This is an educational checklist, not legal advice; some requirements are relaxed for firms holding data on fewer than 5,000 consumers. Assessment provided in partnership with KMicro Tech.